Your IT environment is the backbone of your business—but without proper oversight, hidden risks, security gaps, and compliance issues can go unnoticed.
At Net2Net IT, our comprehensive IT audit services provide a detailed evaluation of your infrastructure, security posture, and operational processes. We identify vulnerabilities, assess compliance, and deliver actionable recommendations to strengthen your systems and reduce risk.
A professional IT audit is a systematic evaluation of your systems, networks, and processes to identify vulnerabilities and ensure compliance with best practices and standards like ISO 27001.
An IT audit is a structured assessment of your organization’s technology environment, designed to:
- Identify security vulnerabilities and risks
- Evaluate existing IT controls and policies
- Ensure compliance with regulatory frameworks
- Improve system performance and reliability
These audits examine everything from infrastructure and access controls to employee practices and incident response capabilities.
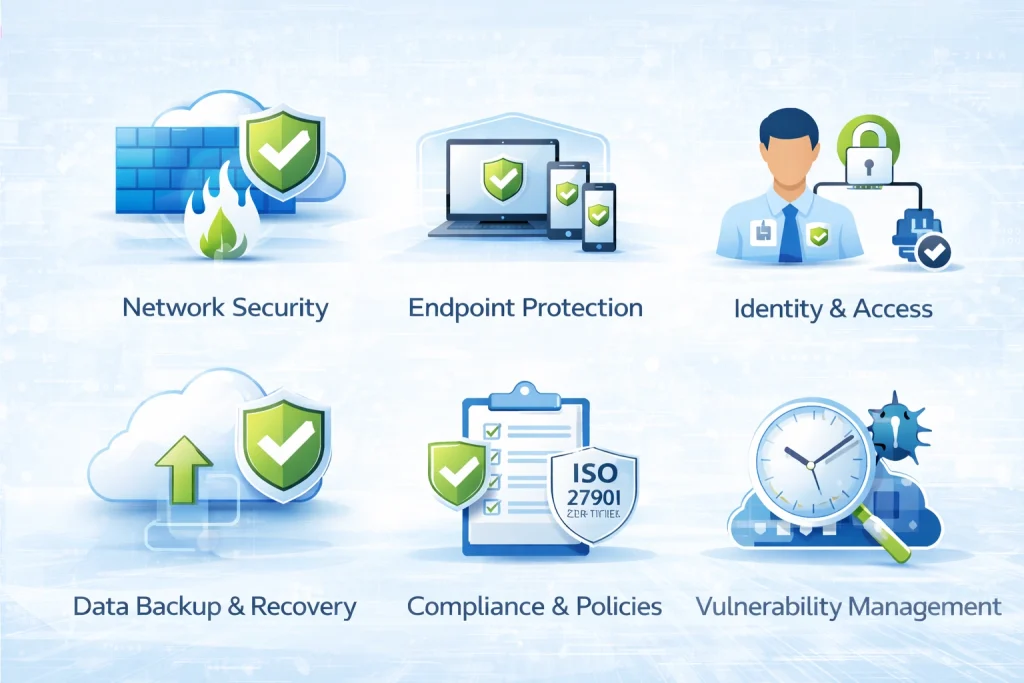
Our IT audits cover all critical areas of your business technology environment to ensure nothing is overlooked.
Infrastructure & Network Security
- Firewalls, switches, and network configurations
- External exposure and attack surface
- Network segmentation and monitoring
Endpoint & Device Security
- Workstations, laptops, and mobile devices
- Patch management and update compliance
- Antivirus, EDR, and endpoint controls
Identity & Access Management
- User permissions and role-based access
- Multi-factor authentication (MFA)
- Privileged account security
Data Protection & Backup
- Backup integrity and recovery testing
- Encryption policies and data handling
- Cloud and on-prem data storage
Security Policies & Procedures
- Acceptable use policies
- Incident response plans
- Security awareness training
Compliance & Regulatory Readiness
- ISO 27001 alignment
- Cyber insurance requirements
- Industry-specific compliance frameworks
A thorough audit evaluates technical controls, policies, and processes across people, systems, and vendors to ensure complete coverage.
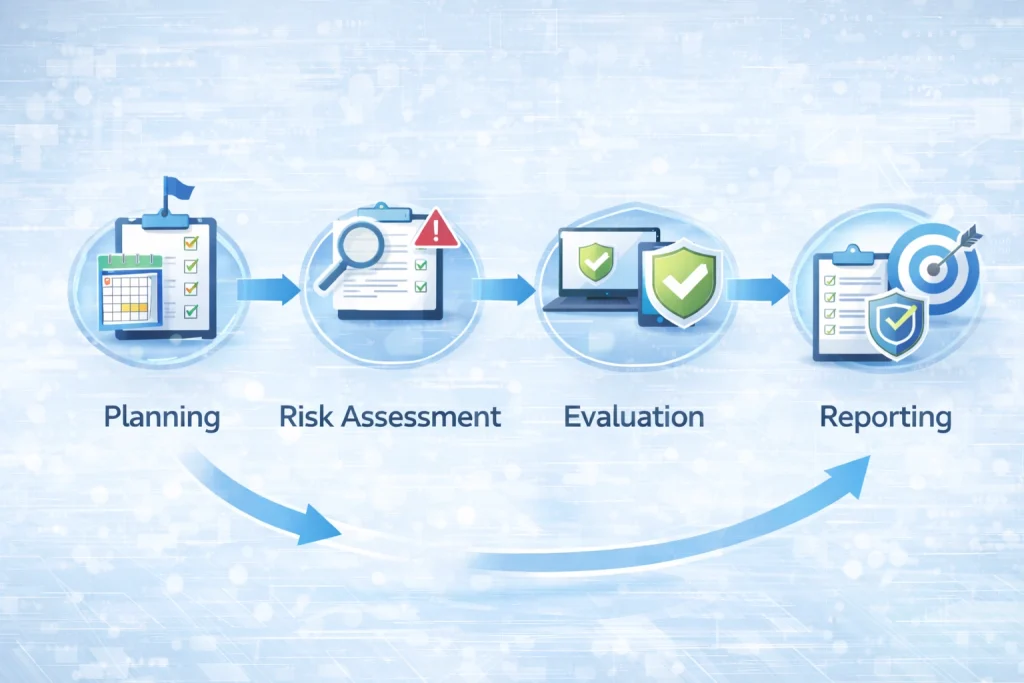
We follow a structured and repeatable methodology to ensure accurate results and meaningful insights.
1. Discovery & Scope Definition
We define the audit scope based on your business goals, regulatory requirements, and risk profile.
2. Data Collection & Analysis
Our team reviews systems, configurations, logs, and documentation to identify gaps and weaknesses.
3. Risk Identification
We identify vulnerabilities, misconfigurations, and operational risks across your IT environment.
4. Testing & Validation
Where required, we perform:
- Vulnerability scans
- Configuration reviews
- Access and control validation
5. Reporting & Recommendations
All findings are documented and prioritized based on risk and business impact, with clear remediation steps.
6. Remediation Planning
We provide a roadmap to address issues, improve security posture, and align with best practices.
After completing your IT audit, you’ll receive a detailed, executive-ready report including:
- Risk Summary & Security Score
- Identified Vulnerabilities & Gaps
- Compliance Status Overview
- Prioritized Remediation Plan
- Strategic IT Recommendations
Audit findings are typically documented with prioritized recommendations to guide remediation and strengthen security controls
A structured infrastructure IT audit and risk assessment helps organizations prepare for cyber security insurance applications and renewals by identifying security gaps, validating key controls, and documenting the current state of the environment. Aligned with recognized frameworks such as ISO/IEC 27001, the assessment reviews critical areas including patch management, access controls, backup and recovery, endpoint protection, and overall security posture. This supports broader compliance initiatives and enables organizations to respond effectively to insurer questionnaires, address underwriting requirements, and strengthen their position for coverage and favourable terms.
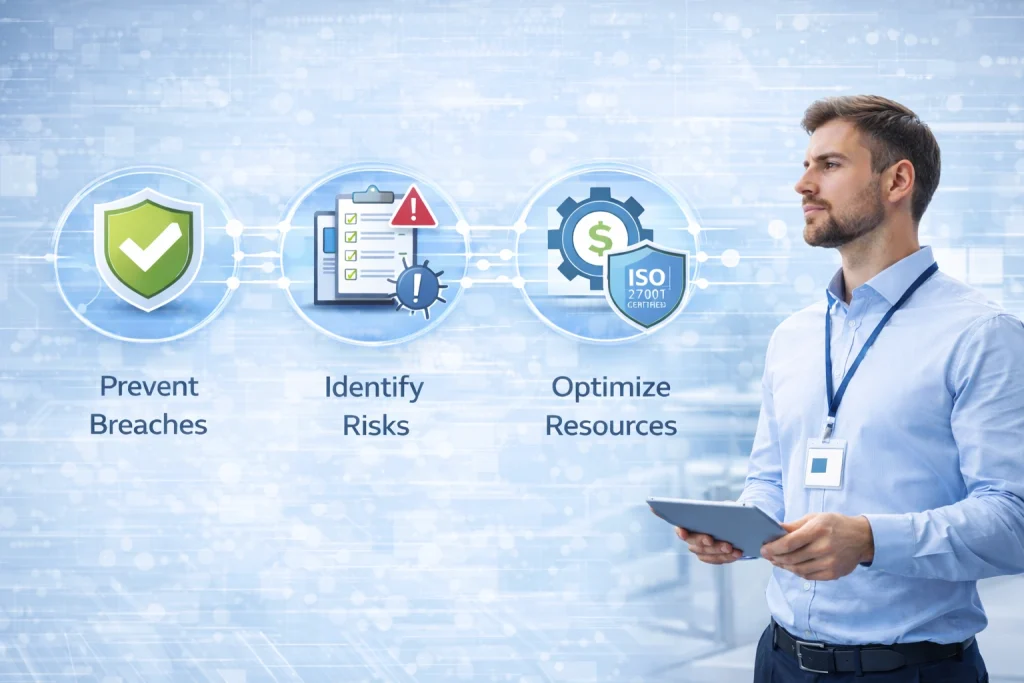
Regular IT audits are essential for maintaining a secure, compliant, and efficient IT environment.
Reduce Cybersecurity Risk
Identify and fix vulnerabilities before they can be exploited.
Ensure Compliance
Meet ISO 27001, SOC 2, and regulatory requirements with confidence.
Improve Operational Efficiency
Eliminate inefficiencies and optimize your IT infrastructure.
Strengthen Business Continuity
Ensure backups, recovery, and incident response plans are effective.
Support Insurance & Due Diligence
Provide documentation required for cyber insurance and audits.
A well-executed audit helps organizations proactively identify risks, validate controls, and prevent costly breaches.
Our IT audit services are ideal for:
- Organizations preparing for ISO 27001 or compliance audits
- Businesses undergoing cyber insurance reviews
- Companies experiencing rapid growth or IT changes
- Organizations concerned about security gaps or vulnerabilities
- Businesses that have never completed a formal IT audit
- Experienced MSP with deep cybersecurity expertise
- Real-world, actionable recommendations—not just reports
- Alignment with industry standards and best practices
- Local support across Toronto and Ontario
- Ongoing support to implement improvements
Get a Complete IT Audit Today
Don’t wait for a security incident or compliance failure to uncover gaps in your environment.
Get a comprehensive IT audit and actionable recommendations to protect your business, improve performance, and ensure compliance.
Contact Net2Net IT today to schedule your IT audit.