Identity-based attacks are now the #1 entry point for cybercriminals. Traditional antivirus and endpoint protection are no longer enough. Our Identity Threat Detection & Response (ITDR) services continuously monitor, detect, and respond to suspicious identity activity across your environment—protecting your business from account takeovers, privilege escalation, and unauthorized access.
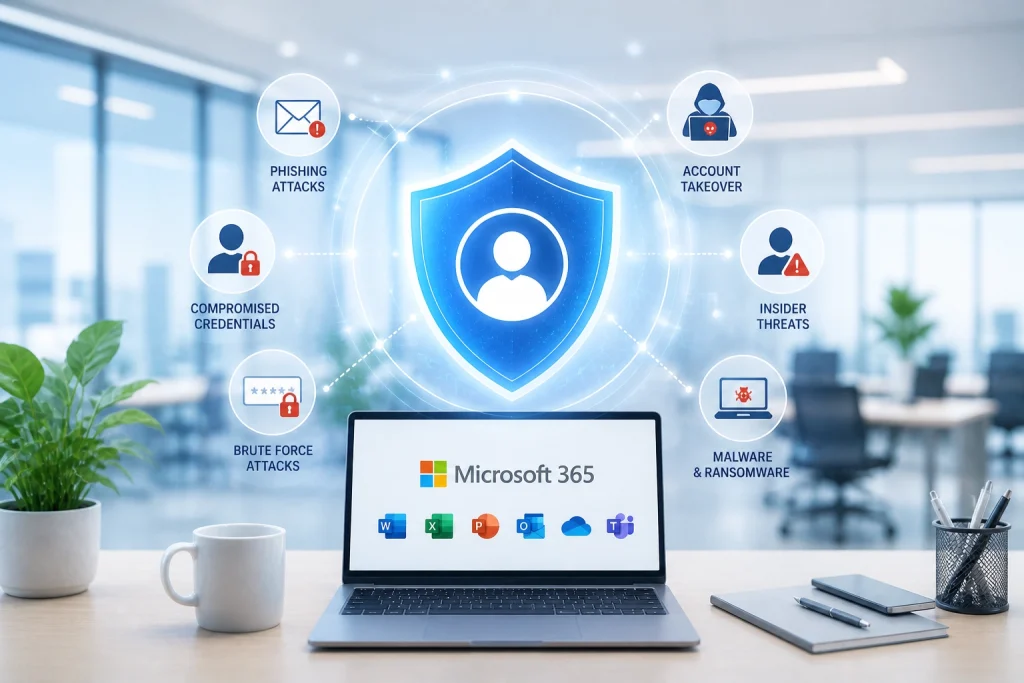
Why Identity Security Is Critical in Today’s Threat Landscape
Modern cyberattacks don’t break in—they log in.
Attackers target:
- User credentials
- Privileged accounts
- Authentication systems
- Cloud identities (Microsoft 365, Entra ID, etc.)
Once inside, they move laterally, escalate privileges, and maintain persistence—often undetected for weeks or months.
ITDR focuses specifically on detecting and stopping these identity-driven attacks in real time.
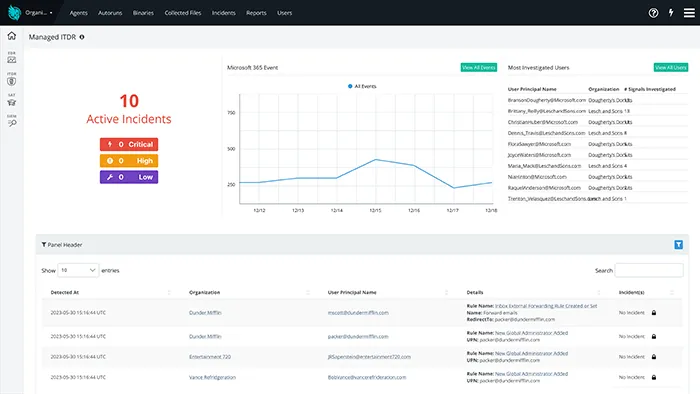
Identity Threat Detection & Response (ITDR) is a specialized cybersecurity layer that protects your organization’s identity infrastructure by:
- Monitoring authentication activity
- Detecting suspicious login behavior
- Identifying compromised accounts
- Responding to threats automatically or with human intervention
Unlike traditional security tools, ITDR is built to protect identities—not just devices.
Key Features of Our ITDR Service
1. Continuous Identity Monitoring (24/7)
We monitor authentication activity across your environment in real time, including:
- Login attempts
- Failed authentication events
- Privilege changes
- Unusual access patterns
This ensures no suspicious behavior goes unnoticed, even outside business hours.
2. Detection of Account Takeovers
We identify signs of compromised accounts such as:
- Logins from unusual locations or impossible travel
- Suspicious IP addresses or TOR usage
- Abnormal login times or patterns
Immediate alerts and response prevent attackers from gaining a foothold.
3. Privilege Escalation Detection
Attackers often attempt to elevate access after initial entry.
We detect:
- Unauthorized admin role assignments
- Sudden privilege changes
- Suspicious group membership modifications
This stops attackers before they gain full control of your environment.
4. Lateral Movement Identification
Once inside, attackers move across systems to expand access.
Our ITDR solution identifies:
- Unusual access to multiple systems
- Credential misuse across endpoints
- Abnormal authentication chaining
This prevents full-scale breaches and ransomware deployment.
5. Persistence Mechanism Detection
Cybercriminals aim to maintain long-term access.
We detect:
- Backdoor accounts
- Hidden authentication methods
- Unauthorized MFA changes
This ensures attackers are completely removed—not just partially contained.
6. Real-Time Threat Response
When a threat is detected, immediate action is taken:
- Account lockdown
- Session termination
- Forced password resets
- Access revocation
Response can be automated or managed by security experts.
7. Integration with Microsoft 365 & Entra ID
Our ITDR service is optimized for modern cloud environments, including:
- Microsoft 365
- Entra ID (Azure AD)
- Hybrid identity environments
This provides deep visibility into your most critical systems.
8. Human-Led Threat Investigation
Not all threats are obvious.
Our security team:
- Investigates suspicious activity
- Validates real threats vs false positives
- Provides actionable remediation steps
You get expert-level analysis without hiring in-house security staff.
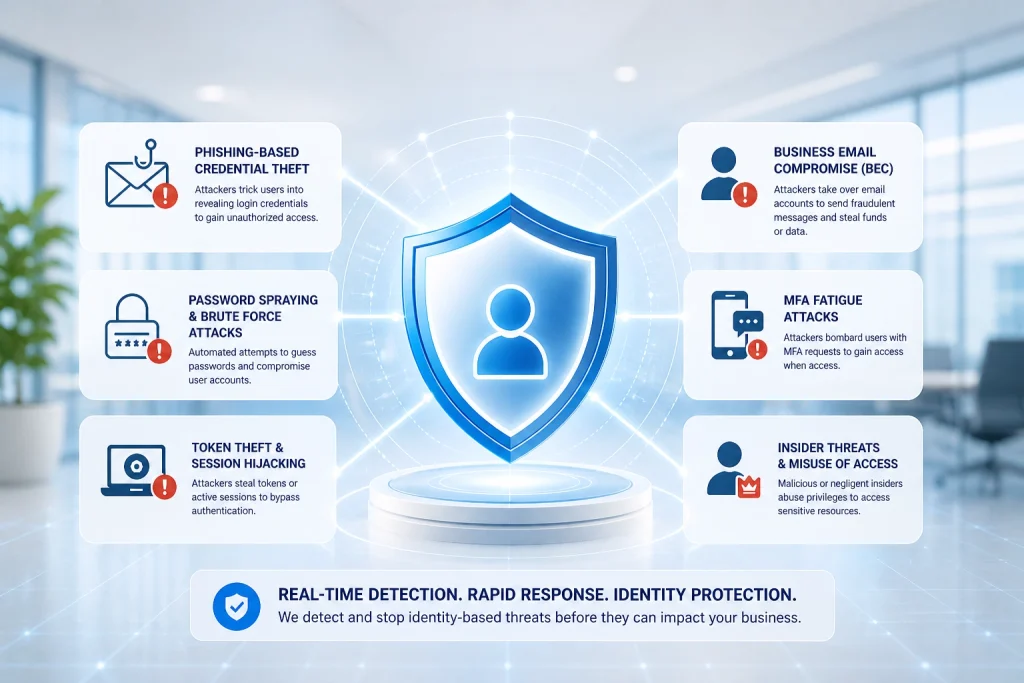
- Phishing-based credential theft
- Business Email Compromise (BEC)
- MFA fatigue attacks
- Password spraying and brute force attempts
- Token theft and session hijacking
- Insider threats and misuse of access
Business Benefits of ITDR
Prevent Costly Data Breaches
Identity attacks often lead to ransomware or data exfiltration. ITDR stops threats before damage occurs.
Improve Compliance Readiness
Supports frameworks like:
- ISO 27001
- Cyber insurance requirements
- Industry security standards
Reduce Risk Across Cloud Environments
Protect Microsoft 365, remote users, and hybrid infrastructures.
Minimize Downtime and Disruption
Early detection means threats are contained before impacting operations.
Enhance Visibility Into User Activity
Understand who is accessing what—and whether it’s legitimate.

Most businesses rely on:
- Antivirus
- Firewalls
- Endpoint Detection & Response (EDR)
These tools do not adequately monitor identity behavior.
ITDR fills this critical gap by focusing on:
- Authentication systems
- User behavior
- Access control
How Our ITDR Service Works
Connect Identity Systems
Secure integration with your cloud and authentication platforms
Baseline Normal Behaviour
Learn what typical user activity looks like
Detect Anomalies
Identify deviations from normal patterns
Alert & Respond
Immediate action to contain threats
Investigate & Report
Detailed analysis and recommendations
ITDR is essential for organizations that:
- Use Microsoft 365 or cloud identity platforms
- Have remote or hybrid workforces
- Handle sensitive data
- Require compliance (ISO 27001, cyber insurance, etc.)
- Want to proactively prevent breaches
A Smarter, Proactive Approach to Cybersecurity
Identity Threat Detection & Response is no longer optional—it’s essential.
By focusing on how attackers actually operate today, ITDR provides:
- Faster detection
- More accurate alerts
- Stronger protection against modern threats
Protect Your Business from Identity-Based Attacks
Don’t wait until credentials are compromised.
Implement a proactive ITDR strategy to:
- Secure user identities
- Detect threats early
- Respond before damage occurs