Managed Services & Technical Support Services

Cybersecurity

Cybersecurity protects your business with advanced technology, monitoring, and employee training. SAT, ITDR, SIEM, and EDR work together to prevent, detect, and respond to threats.

Cyber threats aren’t slowing down. They’re evolving every day — and they’re targeting businesses of every size.

Many organizations depend solely on tools to stop attacks, but the reality is cybercriminals target more than just systems—they go after people, identities, and behaviours. Modern cybersecurity must move beyond antivirus and firewalls. It requires smarter protection, advanced detection, and employees equipped to recognize threats before damage occurs.

Security Awareness Training (SAT), Identity Threat Detection & Response (ITDR), Security Information and Event Management (SIEM), and Endpoint Detection & Response (EDR) form a comprehensive security strategy, protecting your business from every angle.

Rather than reacting after an incident, you gain the tools, training, and visibility needed to identify and stop threats early—before they cause downtime, data loss, or costly breaches.
cybersecurity

What You Gain With Our Cybersecurity Services:

EDR (Endpoint Detection & Response)

Laptops, desktops, and mobile devices are among the most common entry points for cyberattacks. EDR continuously monitors these endpoints for suspicious behavior, detects threats in real time, and helps stop attacks before they spread.

SAT (Security Awareness Training)

Most cyberattacks begin with a simple mistake—such as clicking a malicious link, opening a deceptive attachment, or trusting a message that only appears legitimate. Security Awareness Training empowers employees to spot real threats in everyday scenarios, preventing attacks before they impact your organization.

ITDR (Identity Threat Detection & Response)

Modern cybercriminals no longer need to break in—they can simply log in. ITDR safeguards your business by detecting suspicious login behavior, abnormal account activity, and identity-based threats before they escalate into serious security incidents.

SIEM (Security Information and Event Management)

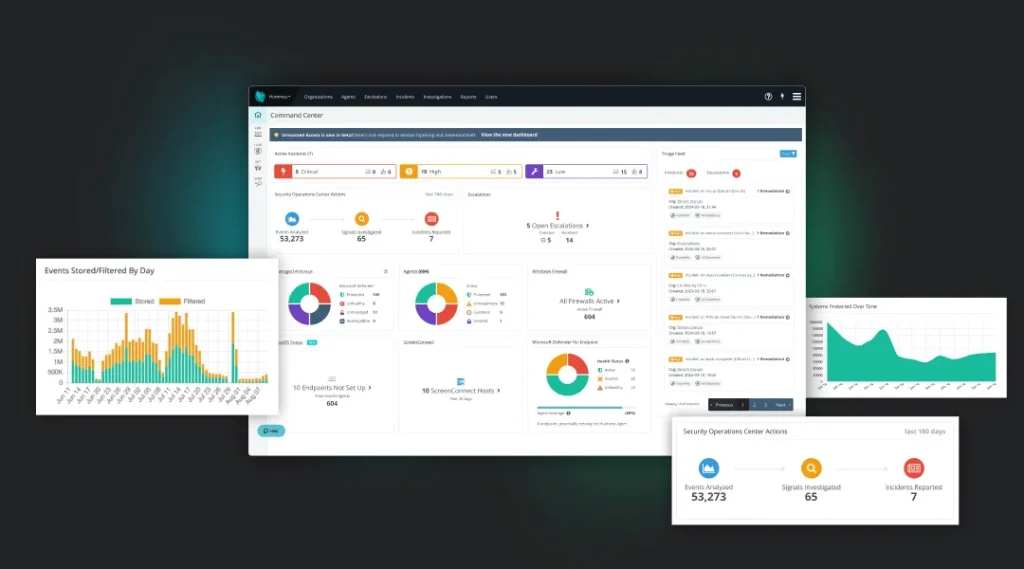
Your systems generate thousands of security events every day. SIEM consolidates all this data in one platform, providing clear visibility across your network and enabling you to detect threats faster and respond with confidence.
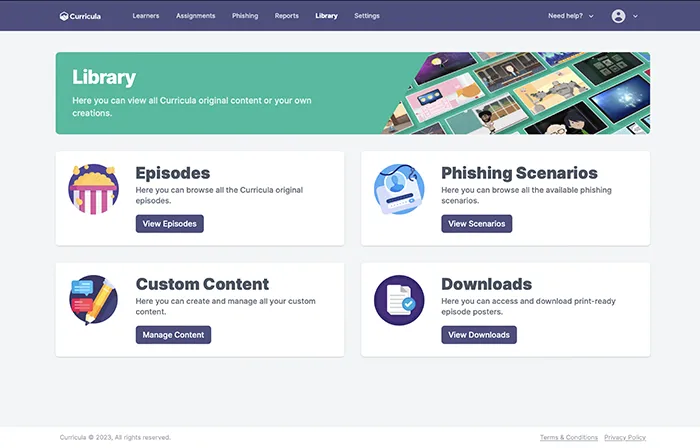
Huntress SAT

Security Awareness Training is one of the most important parts of modern cybersecurity because the majority of cyber incidents start with human error or social engineering. In fact, 74% of breaches involve the human element, including phishing attacks, misuse, or simple mistakes.

SAT trains your employees to recognize real threats before they become real problems. Instead of relying only on technology to catch attacks after they happen, your team learns how to spot phishing emails, suspicious links, and other common attack methods from the start.

Modern Security Awareness Training stands out because it actively engages employees. Interactive, story-driven lessons, simulated phishing attacks, and realistic scenarios ensure that employees retain what they learn and can apply it immediately in their daily tasks. Regularly updated training reflects the latest real-world threats, so your organization is prepared for current risks—not outdated ones.

A well-crafted SAT program not only supports compliance with regulations like HIPAA, PCI, SOC 2, and GDPR, but also fosters a culture where every employee recognizes their responsibility in safeguarding company data.

With Security Awareness Training, human error—often the biggest risk—becomes your organization’s strongest defence.

Have questions or ready to get started?

Cybercriminals are no longer focused solely on breaching networks. Today, the quickest entry point into a business is often through stolen or compromised identities.
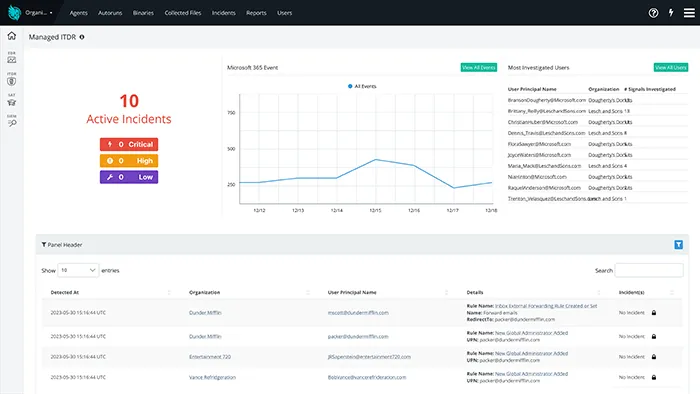
Identity Threat Detection & Response (ITDR) safeguards your organization by continuously monitoring how identities are used across your systems. Rather than waiting until an account has been fully compromised, ITDR identifies unusual activity—such as suspicious logins, abnormal access patterns, or attempts to escalate privileges—enabling faster response.
Huntress ITDR Account Level
This proactive approach helps prevent attacks early, stopping hackers before they can move through your systems, access sensitive data, or deploy ransomware.

ITDR also integrates with Security Awareness Training and Endpoint Detection & Response to deliver a comprehensive security strategy. If an employee clicks a phishing email, ITDR can immediately detect suspicious account activity. If credentials are stolen, unauthorized access can be identified and blocked before any real damage is done.
Identity security is no longer optional. It stands as one of the most critical layers in modern cybersecurity—and remains among the most effective ways to reduce risk.

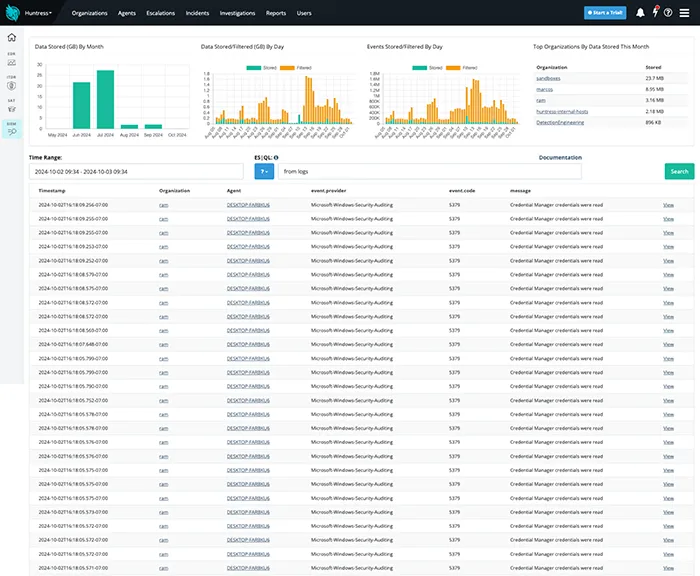
Most businesses generate thousands—or even millions—of security events every day. Without proper tools, distinguishing between significant threats and harmless events becomes nearly impossible.

SIEM (Security Information and Event Management) solutions collect and analyze security data from your entire environment, including logins, user activity, system alerts, and network behavior. Instead of having fragmented information across multiple systems, SIEM consolidates everything into a single, unified view.

The true value of SIEM lies in its visibility. It enables early detection of suspicious behavior, faster responses to potential threats, and a comprehensive understanding of network activity at any given moment.

SIEM also plays a critical role in compliance. Many industries mandate detailed logging and reporting to meet regulatory standards. With SIEM, you gain the insights and reporting capabilities required to remain audit-ready while strengthening your overall security posture.

Instead of reacting blindly to incidents, SIEM empowers your organization with clarity, control, and confidence.

Endpoints are among the most frequent targets for cyberattacks. Devices like laptops, desktops, and mobile phones face ongoing exposure to threats such as malware, ransomware, and phishing attempts.

Endpoint Detection & Response (EDR) surpasses traditional antivirus solutions. Rather than just blocking known threats, EDR continuously monitors endpoint activity to detect suspicious behaviour in real time. As a result, organizations can identify and stop threats—even those that have never been encountered before.
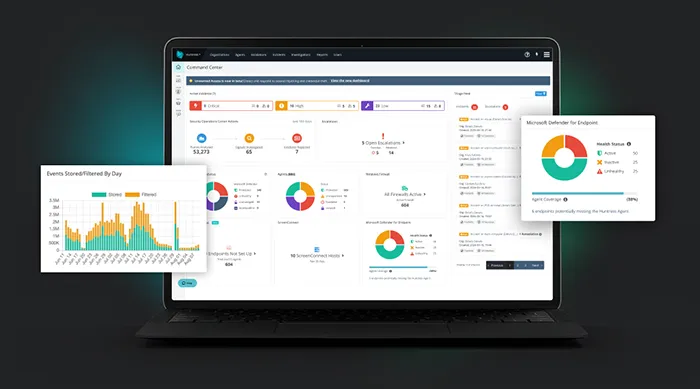
EDR also empowers security teams to investigate incidents efficiently. If a threat is detected, teams gain clear insight into what occurred, how it began, and what actions were taken. This level of visibility enables faster responses, minimizes damage, and helps prevent similar attacks in the future.
When integrated with Security Awareness Training and Identity Threat Detection & Response, EDR becomes a key component of a comprehensive security ecosystem—safeguarding your business from every angle.
 
Have questions or ready to get started?

Explore Our Full Range of Cybersecurity Services

Contact Us

Partner with Us for
Comprehensive Support

At Net2Net, we do more than solve technical problems—we build long‑term partnerships that keep your business secure, efficient, and ready for growth. Our team becomes an extension of yours, providing proactive guidance, rapid response, and the reliable expertise you need to stay ahead in a constantly evolving digital landscape.
When you partner with us, you gain:
End‑to‑End Support

From daily technical assistance to strategic system planning, we cover every layer of your IT environment so you can stay focused on your business.

Proactive Monitoring & Protection

We identify issues before they impact operations, keeping your systems healthy and your data secure.

Flexible, Scalable Solutions

Our services adapt as your business grows—no bottlenecks, no unnecessary upgrades, just smart, future‑proof IT.

Access to Industry Experts

Whether you're managing remote teams, modernizing infrastructure, or planning your next big move, our specialists are here to guide you.

A Trusted Partnership

We believe in clear communication, dependable support, and delivering results you can measure.

Let’s work together to create a technology foundation that strengthens your operations today and positions your business for tomorrow.
Connect With Us

Name(Required)
Company Name (if applicable)
Email(Required)
Please let us know what's on your mind. Have a question for us? Ask away.
HOW WE DO

Our Customer Testimonials

What are
our clients
saying?

Our Technology
Services Stack

Discover the full range of IT services designed to support your business, strengthen your infrastructure, and enhance overall performance. No matter your needs, we provide solutions that keep your technology running smoothly:

Technical Support

Fast, reliable help to resolve issues quickly and keep your systems running smoothly.

Backup and Disaster Recovery

Automated backups and rapid recovery to keep your data safe and your business resilient.

Barracuda Services

Barracuda is a leading global cybersecurity company providing complete protection against complex threats for all sized businesses.

VoIP and Video Conferencing

Modern, reliable communication solutions with clear calling and easy scalability.

Cybersecurity

Cybersecurity protects your business with advanced technology, monitoring, and employee training. SAT, ITDR, SIEM, and EDR work together to prevent, detect, and respond to threats.

Managed IT Services

Proactive management of your IT environment to ensure stability, security, and peak performance.

Microsoft 365 Migrations

Seamless, secure migrations that minimize disruption and maximize productivity.

Monitoring and Alerting

Real‑time system monitoring with instant alerts to catch and address issues before they escalate.

Technical Systems Analysis

In‑depth assessments that reveal risks, inefficiencies, and improvement opportunities.

Virtual Desktop and Apps

Secure, high‑performance virtual desktops and apps accessible from any device, anywhere.