In today’s rapidly evolving threat landscape, businesses are no longer asking if they will face cybersecurity risks—but when. From ransomware attacks to insider threats and misconfigured cloud environments, the modern IT ecosystem presents a wide range of vulnerabilities.
An IT risk assessment is the first and most critical step in identifying, evaluating, and mitigating these risks. It provides organizations with a clear understanding of their exposure and lays the groundwork for stronger security, improved operational resilience, and successful compliance initiatives—including ISO 27001 audits.
For organizations across Toronto and the Greater Toronto Area, implementing a structured risk assessment is not just best practice—it’s a business necessity.
What Is an IT Risk Assessment?
An IT risk assessment is a systematic process used to identify potential threats to your IT infrastructure, evaluate vulnerabilities, and determine the potential impact on your business.
This process helps answer key questions:
- What assets are critical to our business operations?
- What threats could compromise those assets?
- Where are our vulnerabilities?
- What is the likelihood and impact of each risk?
- What controls should be implemented to reduce risk?
The goal is to provide a risk-based decision-making framework, enabling businesses to prioritize security investments effectively.
Why IT Risk Assessments Are Essential
1. Identify Hidden Security Gaps
Many organizations operate under the assumption that their systems are secure—until an incident proves otherwise. Risk assessments uncover vulnerabilities such as:
- Weak access controls
- Lack of multi-factor authentication (MFA)
- Outdated or unpatched systems
- Insufficient logging and monitoring
2. Reduce Cybersecurity Risk
By proactively identifying risks, businesses can implement controls before incidents occur, significantly reducing exposure to:
- Ransomware
- Phishing attacks
- Data breaches
- Insider threats
3. Support Compliance Requirements
Regulatory frameworks and cybersecurity standards—including ISO 27001, PIPEDA, and cyber insurance requirements—require organizations to demonstrate risk management practices.
4. Improve Business Continuity
Understanding risks allows organizations to build stronger disaster recovery and business continuity strategies, minimizing downtime and financial loss.
5. Strengthen Client Trust
Customers and partners increasingly expect organizations to demonstrate strong cybersecurity practices. A formal risk assessment shows maturity and commitment to protecting data.
Key Components of a Comprehensive IT Risk Assessment
A high-quality IT risk assessment follows a structured methodology aligned with frameworks such as ISO 27001.
1. Asset Identification
Identify all critical assets, including:
- Servers and endpoints
- Cloud environments (e.g., Microsoft 365)
- Network infrastructure (firewalls, switches, WiFi)
- Applications and databases
- Sensitive data (PII, financial data)
2. Threat Identification
Evaluate potential threats, such as:
- Cyberattacks (malware, ransomware)
- Unauthorized access
- Human error
- Hardware failure
- Third-party/vendor risks
3. Vulnerability Assessment
Determine weaknesses that could be exploited:
- Missing patches
- Misconfigured systems
- Weak passwords or authentication
- Lack of endpoint protection
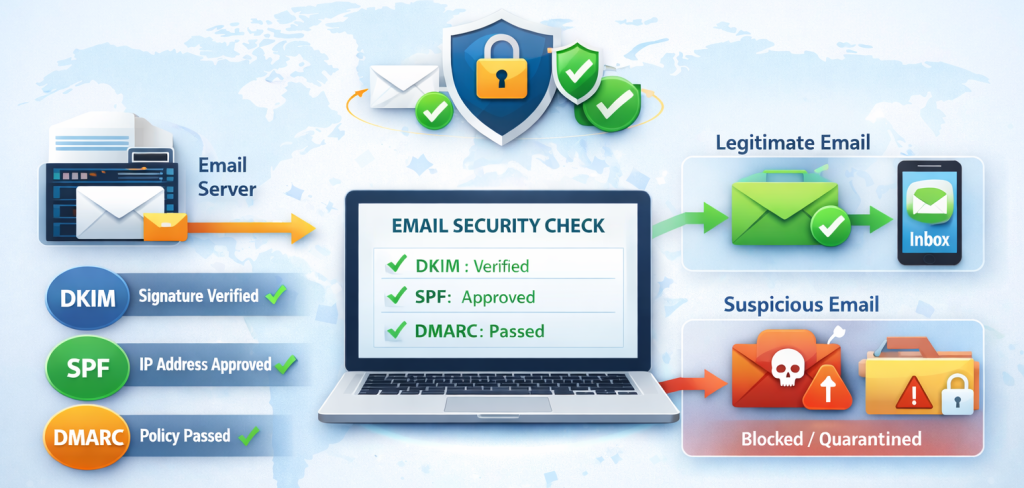
- Poor email security (SPF, DKIM, DMARC gaps)
4. Risk Analysis
Assess each risk based on:
- Likelihood (How probable is it?)
- Impact (What would be the business impact?)
This typically results in a risk matrix or scoring model.
5. Risk Treatment Plan
Define how each risk will be handled:
- Mitigate (implement controls)
- Transfer (insurance)
- Accept (low-risk scenarios)
- Avoid (eliminate risky processes)
How IT Risk Assessments Align with ISO 27001 Audits
The ISO/IEC 27001 standard is globally recognized for Information Security Management Systems (ISMS). At its core, ISO 27001 is risk-driven.
Risk Assessment Is Mandatory
ISO 27001 requires organizations to:
- Identify risks to information security
- Evaluate and prioritize those risks
- Implement appropriate controls (Annex A)
Without a formal IT risk assessment, ISO 27001 certification is not achievable.
Statement of Applicability (SoA)
The results of your risk assessment directly feed into the Statement of Applicability, which defines:
- Which controls are implemented
- Why they are necessary
- How risks are being treated
Continuous Improvement
ISO 27001 is not a one-time effort. Risk assessments must be:
- Reviewed regularly
- Updated as environments change
- Integrated into ongoing security operations
Common Gaps Identified During IT Risk Assessments
Across organizations, several recurring issues are frequently discovered:
- MFA not enforced across all users
- No centralized logging or SIEM solution
- Incomplete endpoint visibility (unmanaged devices)
- Backup systems not regularly tested
- Outdated firewall configurations
- Weak email security controls
- Lack of formal security policies and procedures
- Insufficient user security awareness training
Identifying these gaps early allows businesses to address them before they become costly incidents.
The Role of IT Risk Assessments in Cyber Insurance
Cyber insurance providers are becoming increasingly strict in their requirements. Many now mandate:
- Multi-factor authentication (MFA)
- Endpoint detection and response (EDR)
- Regular patch management
- Documented risk assessments
A well-documented IT risk assessment can:
- Improve eligibility for coverage
- Reduce premiums
- Simplify underwriting processes
Integrating Risk Assessments with Managed IT Services
For many businesses, conducting and maintaining risk assessments internally can be challenging. Partnering with a Managed Service Provider (MSP) like Net2Net IT ensures:
- Continuous monitoring of risks
- Proactive vulnerability management
- Alignment with compliance frameworks
- Integration with tools like Microsoft Defender, Huntress, and SIEM platforms
This transforms risk assessments from a one-time exercise into an ongoing security strategy.
Best Practices for Effective IT Risk Assessments
To maximize value, organizations should:
- Conduct assessments at least annually (or after major changes)
- Use standardized frameworks (ISO 27001, NIST)
- Include both technical and operational risks
- Document all findings and remediation actions
- Implement a scoring system for prioritization
- Regularly review and update risk registers
Why Choose Net2Net IT for IT Risk Assessments and ISO 27001 Readiness?
At Net2Net IT Solutions, we deliver comprehensive, compliance-driven IT risk assessments designed to:
- Identify security gaps across your entire environment
- Align your organization with ISO 27001 requirements
- Support cyber insurance readiness
- Provide clear, actionable remediation plans
- Deliver executive-level reporting and risk scoring
Our approach combines deep technical expertise with real-world business understanding—ensuring your organization is secure, compliant, and prepared for future growth.
Conclusion
An IT risk assessment is more than just a security exercise—it’s a strategic initiative that protects your business, ensures compliance, and builds resilience against modern threats.
Whether you are preparing for an ISO 27001 audit, improving your cybersecurity posture, or meeting cyber insurance requirements, a structured risk assessment is the foundation for success.